Banking Data Modernization
Databricks Banking Case Study: From Siloed Data to Trusted Decisions
A representative banking modernization case study showing how a governed Databricks lakehouse can improve fraud detection, risk reporting, and customer intelligence.
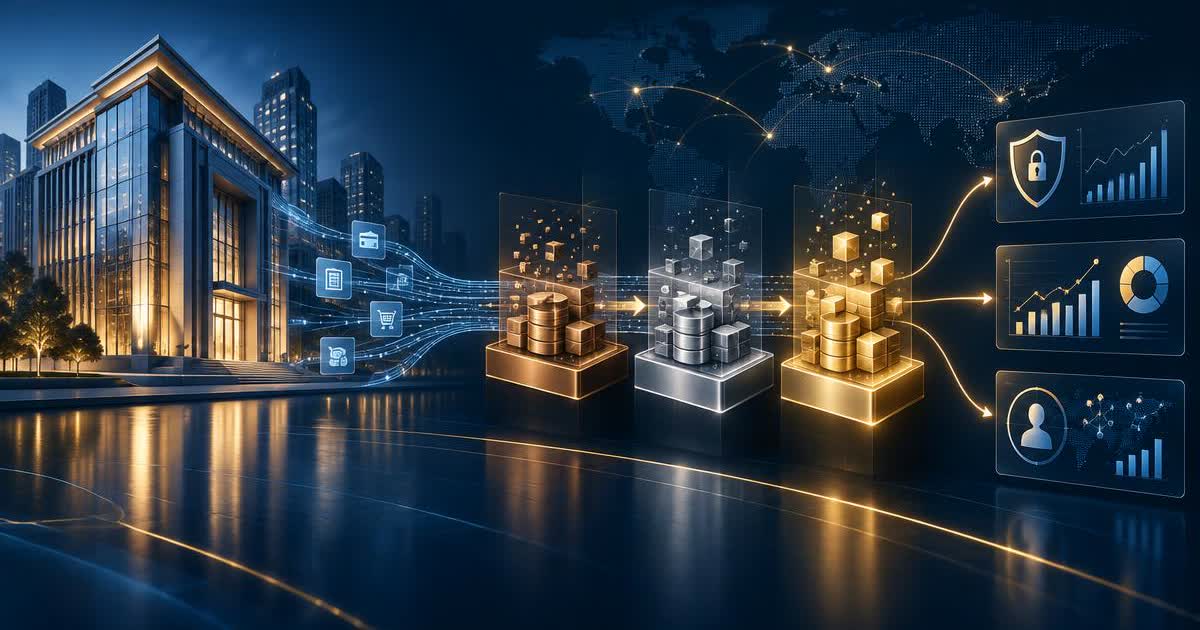
A mid-sized bank had grown around separate systems for core banking, cards, digital channels, lending, and customer service. Each team reconciled its own extracts, slowing risk reporting and making it difficult to act on fraud signals or understand a customer across products.
The challenge: trusted answers arrived too late
Overnight processing moved data through fragile file transfers and tightly coupled scripts. A change in one source could delay regulatory reports, while investigators often worked from partial customer and transaction histories.
Slow reporting
Risk and finance teams waited for sequential jobs and manual reconciliation before reports could be approved.
Fragmented visibility
Accounts, cards, loans, and digital activity could not be viewed through one governed customer record.
Control overhead
Sensitive fields were copied into multiple systems, increasing access reviews and audit effort.
Delayed signals
Fraud rules operated on incomplete or older data, limiting timely investigation and intervention.
The solution: a governed banking lakehouse
The proposed platform used Databricks to create one governed path from operational data to reporting, detection, and analytics. The design preserved source evidence while giving each domain a reusable, quality-controlled data product.
Bronze
Preserve the record
Land immutable transactions, account changes, card events, and channel logs with source timestamps and audit metadata.
Silver
Build trusted entities
Validate schemas, tokenize sensitive identifiers, resolve customers, deduplicate events, and standardize transaction semantics.
Gold
Serve banking outcomes
Publish governed products for liquidity, credit risk, fraud operations, regulatory reporting, and customer intelligence.
Batch ingestion handled daily ledger and reference extracts. Streaming pipelines processed card authorizations, mobile events, and payment activity where minutes mattered. Shared identifiers connected those paths without exposing raw personal data to every consumer.
Security and governance were designed first
Banking data requires more than perimeter controls. The design applied least-privilege access, separated duties, and made every sensitive use observable.
- Classify personal, financial, and authentication data as it enters the platform.
- Mask or tokenize sensitive values before broad analytical use.
- Apply catalogue, schema, table, row, and column controls to match business responsibilities.
- Record lineage from source transactions through calculations and published reports.
- Separate development, testing, and production, with controlled promotion and audit evidence.
- Define retention and deletion policies for each banking domain and jurisdiction.
Three use cases created the first business value
Fraud investigation
Combine authorization events, device signals, account history, and known patterns into a near-real-time investigator view. Alerts include the evidence needed to prioritize and explain a review.
Risk and regulatory reporting
Create versioned, traceable data products with reconciliation rules and approval checkpoints, reducing repeated preparation across finance and risk teams.
Customer intelligence
Build a permission-aware customer view across deposits, lending, cards, and digital interactions to support service decisions without creating uncontrolled copies.
A phased delivery reduced migration risk
How the bank would measure success
Because this scenario is representative, targets should be baselined against the bank’s current operation rather than presented as guaranteed outcomes. A practical scorecard would track:
- Time from source event to a usable fraud or operational signal.
- Regulatory-report preparation time and reconciliation exceptions.
- Pipeline success, freshness, recovery time, and missed service levels.
- Percentage of critical datasets with owners, quality contracts, and lineage.
- Compute and storage cost per domain data product.
- Analyst time spent locating, joining, and validating data.
What banking leaders should take from this case
The strongest modernization programmes do not begin by moving every table. They begin with a small number of important decisions, then build the governed data products and operating controls those decisions require.
For banks, trust is the architecture: source evidence, reconciliation, access control, lineage, recovery, and accountable ownership must advance with each use case. A platform only creates value when teams can use its outputs confidently.
Modernize with control
Plan your first governed banking data product.
EdgeWave can assess your priority use case, source landscape, security requirements, and delivery risks, then shape a practical Databricks roadmap.
Discuss your banking use case